A July 27 letter from Senator Ron Wyden asks three federal agencies to mandate, within two years, the replacement of internet-facing VPN appliances across the U.S. government — arguing that reactive emergency patching has become an unsustainable substitute for structural reform.
By Vladimir Tsakanyan, PhD | Director, Center for Cyber Diplomacy and International Security (CCD-IS)
On July 27, 2026, Senator Ron Wyden sent a letter to the Office of Management and Budget, the Cybersecurity and Infrastructure Security Agency, and the National Institute of Standards and Technology urging a coordinated, binding effort to remove legacy, internet-facing virtual private network appliances from federal networks within two years. The letter is not a request for further study. It sets out specific actions for each agency, framed around a single argument: that federal cybersecurity teams have been trapped, in Wyden’s words, in an endless game of “whack-a-mole,” repeatedly issuing emergency directives and accelerated patch mandates against a category of device that is structurally exposed by design. As of this writing, none of the three agencies has publicly responded.
The Proposal’s Four Parts
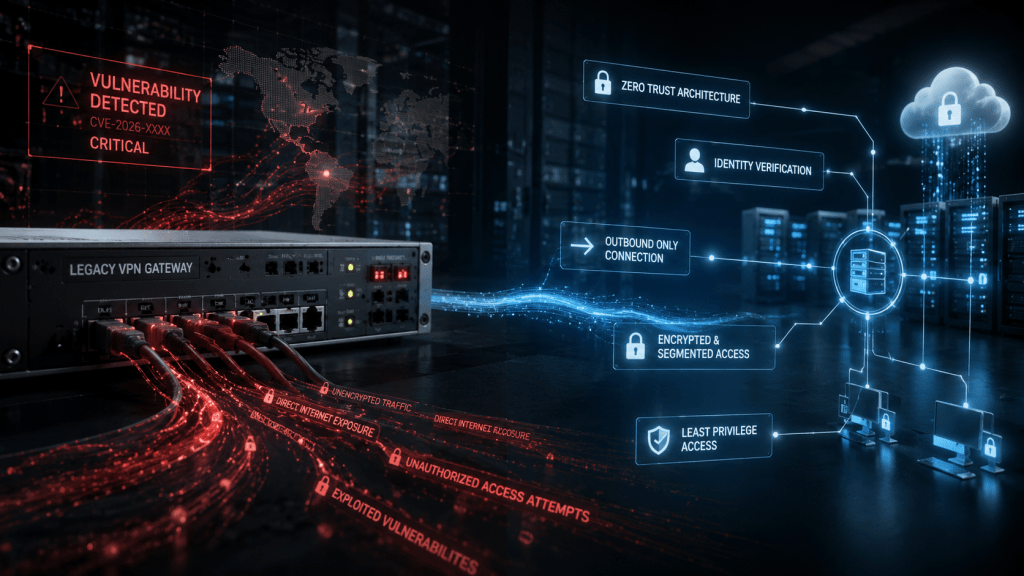
The letter asks CISA to issue a Binding Operational Directive requiring civilian federal agencies to eliminate public-facing legacy VPN appliances within two years, replacing them with zero-trust remote-access architecture. It separately urges the National Security Agency, acting under the Defense Department’s existing authorities rather than the letter’s three named recipients, to impose the same two-year deadline across military, intelligence, and other national security networks. For NIST, the letter requests technical implementation standards defining what a compliant zero-trust remote-access system must include: outbound-only connection architecture, software written in memory-safe programming languages, agency-controlled rather than vendor-controlled encryption keys to limit supply-chain exposure, and alignment with ongoing post-quantum cryptography migration. For OMB, the letter asks for two things — that zero-trust investment be prioritized in the federal budget process, and that procurement rules be updated so that agencies and defense contractors may only purchase remote-access products from vendors that formally certify compliance with the new NIST standards.
That last request is the one most likely to have effects beyond the federal government itself. A procurement rule conditioning eligibility to sell to federal agencies and their contractors on zero-trust certification would give NIST’s standards leverage over the broader commercial market for VPN appliances, firewalls, and other network-edge products, not only the subset currently deployed inside government networks.
The Evidentiary Basis
Wyden’s letter grounds the request in a specific pattern rather than a general concern: a series of major intrusions traced to vulnerabilities in VPN and network-edge products from vendors including Cisco, Fortinet, Ivanti, and Check Point, which the letter attributes in significant part to Chinese and Russian state-sponsored actors gaining administrative access to government and contractor networks. The letter cites third-party ransomware-trend reporting to argue that a large share of ransomware-related intrusions in the past year trace back to compromised remote-access infrastructure of this kind. Its central structural claim is that CISA’s current posture — emergency directives and hyper-accelerated patch mandates issued after each new appliance vulnerability is disclosed — treats a design flaw as if it were a series of unrelated incidents, and that no amount of faster patching resolves an architecture that is exposed to the public internet by construction.
That argument is not made in a vacuum. CISA issued Binding Operational Directive 26-04 in June 2026, setting its most aggressive patching timeline to date — a three-day window for remediating the highest-risk vulnerabilities. Wyden’s letter, coming five weeks later, can be read as arguing that even that accelerated timeline confirms rather than resolves the underlying problem: the pace of emergency response has increased because the volume and severity of edge-device compromises has increased, not because the exposure itself has been reduced.
Extending an Existing Architecture
The request builds on a federal zero-trust push that predates this letter by several years. A May 2021 executive order directed federal civilian agencies to adopt zero-trust architecture, and OMB followed with a strategy setting specific implementation goals for agencies to meet by the end of fiscal year 2024. Wyden’s letter does not propose a new federal cybersecurity framework; it argues that the existing zero-trust mandate has left one of its most exposed components — internet-facing remote-access appliances — largely untouched, and it seeks to close that gap through a binding deadline rather than continued voluntary migration. The specific technical requirements it asks NIST to codify, particularly agency-controlled encryption keys and post-quantum alignment, would extend the zero-trust framework’s scope from access control and identity verification into the cryptographic and supply-chain dimensions of remote-access infrastructure specifically.
Outlook
Of the letter’s four requests, a CISA Binding Operational Directive is the one most within a single agency’s power to issue unilaterally and on a relatively short timeline, making CISA’s response the clearest near-term indicator of whether the proposal gains traction. NIST’s request is a longer standards-development undertaking, and OMB’s procurement rule change would need to move through budget and rulemaking processes that typically span multiple cycles. The NSA request sits outside the letter’s three formal recipients entirely, depending instead on the Defense Department’s own decision to act under its existing authorities — a decision that would need to be read alongside the department’s other recent moves on contractor and network cybersecurity requirements. Whether the two-year deadline holds, in whole or in part, will depend less on the technical merits Wyden’s letter lays out, which draw on a well-documented pattern of edge-device compromises, than on whether OMB is willing to attach a compliance deadline with real budget and procurement consequences to a migration that federal agencies have so far pursued unevenly under voluntary guidance.
About the Author Vladimir Tsakanyan, PhD, is a political scientist and strategic analyst specializing in cyber diplomacy and international security. He is Director of the Center for Cyber Diplomacy and International Security (CCD-IS). ORCID: 0000-0002-9349-1907.
Sources
- Senator Ron Wyden, letter to OMB, CISA, and NIST on legacy VPN phaseout (July 27, 2026)
- The Record (Recorded Future News), “Outdated VPNs should be purged from federal agencies, senator says”
- CyberScoop, “Sen. Wyden urges feds to discard older, insecure, public-facing VPNs”
- CyberInsider, “Wyden calls for federal ban on legacy VPNs over security concerns”
- TechTimes, “Wyden Demands Two-Year Federal VPN Purge: Zero-Trust Procurement Rule Would Reshape Vendor Market”
- GovInfoSecurity, “Wyden Calls for Edge Device Annihilation in US Government”

Leave a comment